
MX, SPF, DKIM, and DMARC are the DNS records to publish when a domain sends or receives mail. MX names the servers that accept inbound mail. SPF lists who may send, DKIM signs each message, and DMARC tells receivers what to do when those checks do not align with the From domain, plus where to send reports.
Set them after you buy a domain and before warmup or cold campaigns. A sending platform does not replace the records at your DNS host.
This guide covers what each record does, when to add it, how to publish it, and how to check the result, including email deliverability setup for SPF, DKIM, and DMARC.
What these records are
Why they matter
When to set them up
Step-by-step instructions for MX, SPF, DKIM, and DMARC
What are MX, SPF, DKIM, and DMARC records
SPF, DKIM, and DMARC authenticate mail. MX only routes inbound mail. The notes under the table are the parts people mix up.
| Record | DNS type | What it does |
|---|---|---|
| MX | MX | Routes inbound mail to a mail server |
| SPF | TXT | Lists hosts allowed to send for the domain |
| DKIM | TXT | Publishes the public key for the signature on the message |
| DMARC | TXT | Sets policy and reporting when SPF or DKIM fails to align |
MX (Mail Exchange) records
Purpose. Directs inbound mail to your domain's mail servers.
How it works. MX records name the servers that accept mail for your domain, with a priority on each one. They do not authenticate outbound mail. Outbound delivery uses the recipient's MX, not yours. You still need your own MX so replies, bounces, and DMARC reports can arrive.
SPF (Sender Policy Framework)
Purpose. Names the hosts allowed to send mail for the domain, which is how a receiver spots a forged envelope sender.
How it works. An SPF record lists the IPs and includes allowed to send for the domain. The receiver compares the connecting IP with that list. A match is an SPF pass for the envelope domain, and DMARC still requires alignment with the From domain. The check does not by itself put mail in the inbox.
DKIM (DomainKeys Identified Mail)
Purpose. Confirms the message was signed by a holder of the private key and was not altered in transit.
How it works. DKIM adds a signature that names a selector. DNS publishes the matching public key. The receiver checks the message against that key. The private key stays on the signer. A valid signature shows the message was not altered after signing. Inbox trust still depends on the rest of your sending.
DMARC (Domain-based Message Authentication, Reporting, and Conformance)
Purpose. Sets what receivers should do when mail fails to align, and where they should send reports.
How it works. DMARC uses SPF and DKIM, then checks alignment with the domain in the From header. The check passes when at least one of those two passes and aligns. It does not require both to pass. You choose a policy: none (monitor), quarantine, or reject. Reports show you mail that used your domain, including mail you did not send.
When to Set Up MX, SPF, DKIM, and DMARC
Do this after you buy a domain and before warmup. If Cloudflare or another company holds the nameservers, edit the zone there, not at the registrar that only points the domain away.
Add MX so the domain can receive mail, using the targets from your mailbox provider.
Publish one SPF TXT record that includes every service allowed to send.
Turn on DKIM at the mailbox provider and publish the TXT it gives you.
Publish DMARC at p=none, read the reports, then tighten the policy.
Confirm the lookups and a test message, then warm the mailbox before cold volume.
If the domain already sends, add whatever is missing before you raise volume. Start DMARC at p=none so a broken SPF or DKIM record does not tell receivers to reject your own mail.
Why should Cold Email Senders do Email Authentication?
The benefit is a published identity receivers can test. Open rates and reply rates still depend on the list, the offer, and whether the message was seen.
What providers check
Google's SPF setup says receiving servers check the SPF record to see whether the message came from an authorized server. Microsoft's SPF setup says destination systems do the same for the envelope sender. Missing records leave that test with nothing to pass.
Sender reputation
Authentication is one input providers can store against your domain. A domain that signs mail and publishes a policy is easier to tell apart from a spoofed one. Reputation still moves with complaints, volume, and list quality over time.
Prevent spoofing
Without SPF, DKIM, and DMARC, someone else can send mail that looks like your domain. That forges the brand and can poison reputation you did not build. The three records are how you tell receivers which mail you will stand behind, and what to do with the rest.
What still has to earn the reply
Authentication answers whether this domain sent the message. The reply still depends on the list and the copy.
Setting Up MX Records on Your Server
For Google Workspace, use Google's MX setup. For Microsoft 365, use Microsoft's DNS records guide. Copy the mail hosts and priorities from those pages. The steps below are the panel workflow. The host name mail.yourdomain.com is only a shape, not a value to publish unless your provider told you to.
Follow these five steps to set up MX records:
Access your domain registrar
Log in to the DNS host for the domain (for example GoDaddy, Namecheap, or Cloudflare) and open the DNS settings.
Locate the MX records section
In the DNS management area, find the section to add or manage MX records.
Add new MX records
Add a record, choose MX as the type, and enter the mail server from your provider. A generic shape looks like mail.yourdomain.com. Google and Microsoft each publish their own hosts and priorities. Use those when the mailbox lives there.
Set priority
Assign a priority to each MX record. Lower numbers are higher priority. Repeat for every host the provider lists.
Save changes
Save the MX records. Query the domain and confirm the hosts match your provider before you rely on them.
After that, mail for the domain routes to the servers you named.
Setting Up SPF Record on Your Server
For Google Workspace, use Google's SPF setup. If Google Workspace is the only sender, that page says to copy v=spf1 include:_spf.google.com ~all. The same page recommends ~all.
For Microsoft 365, use Microsoft's SPF setup. If Microsoft 365 is the only sender, that page gives v=spf1 include:spf.protection.outlook.com -all. Microsoft recommends -all for Microsoft 365 domains on that page, together with DKIM and DMARC. Paste a string only when that provider sends the mail and the linked page still shows it.
Access your domain's DNS settings
Open the same DNS host you used for MX.
Create or edit your SPF record
Look for an existing SPF TXT record, one that starts with v=spf1. If it is missing, add one. If it is present, edit that record. Microsoft's SPF setup says only one SPF TXT is allowed per domain. A second one makes the check return a permanent error.
Add each sender your provider documents, as an include: or an ip4: mechanism, on that single record. End with -all or ~all. Do not end a real sending domain with +all.
Illustration, not a record to publish: v=spf1 ip4:192.168.0.1 include:sendgrid.net ~all
Microsoft's SPF setup says an SPF check that needs more than 10 DNS lookups returns a permanent error. Each include: counts as at least one lookup, and a nested include adds more. An ip4: or ip6: value does not count as a lookup.
Save and apply changes
Save the record. Google's SPF setup says it can take up to 48 hours for SPF authentication to start working. Query the TXT before you send.
Test your SPF record
Use an SPF check such as MxToolBox, or Google's SPF check, and confirm the record names the servers that actually send.
Setting Up DKIM Record on Your Server
For Google Workspace, use Google's DKIM setup. For Microsoft 365, use Microsoft's DKIM setup. Other providers use the five steps below. Publish the TXT the provider shows you. Do not invent the key.
Generate your DKIM key pair
Generate a public and private key pair. Most mailbox providers generate the pair and show you the public TXT to publish. If yours does not, OpenSSL can create a pair. The private key stays on the signer. DNS gets the public key only.
Google's DKIM setup says that after you turn on Gmail, you must wait 24 to 72 hours before the Admin console will generate the key.
Access your domain's DNS settings
Open the same DNS host.
Create a new TXT record for DKIM
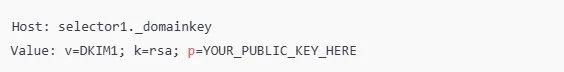
Add a TXT record. In the host or name field, use the selector your provider gives you, followed by ._domainkey. If the panel appends the domain for you, enter that selector host and not the full name, or you will publish a doubled host that never matches.
Google's DKIM setup says the default prefix is google, so the host is google._domainkey, unless that selector is already in use. A name such as selector1._domainkey is only a shape until your provider gives you the real selector.
In the value field, paste the public key. Google's page formats it as v=DKIM1; k=rsa; p= and then the key data. Use the value your provider displays.
More than one sending server is normal. Each signer gets its own selector and TXT. Do not put two private keys on one selector. SPF stays a single TXT.
Save and apply changes
Save the TXT record. Google's DKIM setup says that after you add the key, it can take up to 48 hours for DKIM authentication to start working. Query the selector before you send.
Test your DKIM setup
Use a checker such as DKIMCore, Google's Check MX tool, or MxToolbox. Confirm the selector you sign with is the selector that answers in DNS.
Setting Up DMARC Record on Your Server
For Google Workspace, use Google's DMARC setup. For Microsoft 365, use Microsoft's DMARC setup. Publish SPF and DKIM first. DMARC reads those results.
If you send mail in volume, publish a DMARC record and start by monitoring. Google's DMARC setup says to allow 48 hours after SPF and DKIM are authenticating before you turn DMARC on.
Know the DMARC policy options
None (p=none): monitors mail and does not change delivery. Google's DMARC setup recommends this while you test.
Quarantine (p=quarantine): asks receivers to treat failing mail as spam or junk.
Reject (p=reject): asks receivers to block failing mail.
Move to quarantine or reject after reports show your own mail aligns.
Log in to your DNS host
Open the same DNS host that holds the zone.
Create a new TXT record for DMARC
In the host or name field, enter _dmarc if the panel appends the domain. If it stores the name exactly as typed, use _dmarc.yourdomain.com. Google's DMARC setup says some hosts add the domain name for you, and you should verify the published name. A doubled host (_dmarc.yourdomain.com.yourdomain.com) will not be found.
In the value field, a starter shape is v=DMARC1; p=none; rua=mailto:your-email@domain.com. Replace your-email@domain.com with a mailbox you control. Google's sample record on that page also includes pct, adkim, and aspf. Copy extra tags from that page if you need them. Do not publish the sample addresses.
Alignment decides the result. Google's DMARC setup says the message passes when SPF passes and aligns, or when DKIM passes and aligns. It fails when both of those fail. Relaxed alignment is the default: a subdomain can align with the organizational domain. Strict alignment requires an exact match, and Google notes that strict mode can reject mail from subdomains. A pass on both checks still fails DMARC if neither one aligns with From.
Optional DMARC tags
Aggregate reports (rua). The mailbox that receives summary reports. Google's DMARC setup recommends including rua.
Forensic reports (ruf). Google's DMARC setup says Gmail does not support the ruf tag. Other receivers may. Set rua first.
Save and test your DMARC record
Save the record. Query _dmarc after you save. Check it with a DMARC tester such as DMARC Analyzer or MXToolbox, then send a message and read the Authentication-Results header.
Crosschecking Email Authentication
Use one of these checks after you have queried the new records. If you searched a specific domain plus "MX SPF DKIM", run the lookup on that name. This page does not publish another company's live records.
Check email headers
Send a test to an inbox you can open and read the headers:
Received-SPF: pass means the SPF check passed for that hop.
Authentication-Results: read spf=, dkim=, and dmarc= on their own. dmarc=pass is the DMARC result. spf=pass and dkim=pass are not enough for DMARC when neither identifier aligns with the From domain.
Use a DNS tool
MXToolbox and Google Apps Toolbox can query SPF, DKIM, and DMARC for the domain.
Check provider settings
Many mailbox providers have a domains or settings screen for these records. A correct setup usually shows a verified state. Treat that as a hint, then confirm with a header from a real test message.
Use the command line
nslookup queries DNS from the command line. It can show MX records and the TXT records used for SPF, DKIM, and DMARC.
SPF: nslookup -type=txt yourdomain.com. When the domain sends only through Google Workspace, Google's SPF setup page shows v=spf1 include:_spf.google.com ~all. If nothing comes back, the record is missing or not visible yet. Do not paste that string unless Google is a sender and the page still shows it.
DKIM: nslookup -type=txt selector._domainkey.yourdomain.com. Replace selector with the one you sign with. On Google's DKIM setup page the default host is google._domainkey.
DMARC: nslookup -type=txt _dmarc.yourdomain.com
MX: nslookup -type=mx yourdomain.com
Fix failures
If a check fails, edit the DNS record that check uses. SPF failures are often a missing include, a second SPF record, or too many DNS lookups (see the 10 lookup note in the SPF section). DKIM failures are often the wrong selector or a doubled host name. DMARC failures are often a missing record, or a pass that does not align with From.
Email Warm-Up: The Next Step after Email Authentication
After MX, SPF, DKIM, and DMARC are in place, warm the mailbox before you raise cold volume. A new domain with correct DNS is still a new domain. Do not jump to full campaign volume the day the lookups look right.
Manyreach includes Manywarm, adaptive warmup that adjusts to sender reputation. Paid Business and Agency plans include unlimited credit-free warmup. On Pay As You Go, warmup uses credits: 1 credit covers 10 warmup emails. The ramp itself is covered in email warmup.
FAQs
How do I configure SPF, DKIM, and DMARC?
Publish one SPF TXT record, publish a DKIM TXT for each selector you sign with, then add a DMARC TXT at _dmarc starting at p=none. Confirm each one with a lookup and with Authentication-Results on a test message.
How do I add a DKIM or DMARC record to DNS?
DKIM is a TXT at selector._domainkey. DMARC is a TXT at _dmarc. Paste the value your provider or policy calls for, save, and query the full hostname so you know the panel did not double the name.
Can DKIM cover multiple sending servers?
Yes. Give each server its own selector and its own TXT. Keep SPF as one record and add each sender with include or ip4 on that single record.
Do I need a DMARC setup service?
No. You can publish the TXT yourself. A service can store the rua reports and draw charts. The record at your DNS host is what receivers read.
Where do vendor SPF includes come from?
Copy the include from that vendor's current DNS help onto your one SPF record. This page quotes only the Google Workspace and Microsoft 365 strings, next to the setup pages they come from. Do not paste the illustration in the SPF section.
 Share Article